Dark web markets still move stolen corporate credentials, session cookies, and network access every single day in 2026. Most public lists you find are outdated, full of dead links, or written for curiosity seekers instead of people who actually have to defend networks.
Core Monitoring Checklist (Start here)
- Use only automated CTI platforms or isolated, legally approved research environments.
- Prioritize stealer-log, credential, and initial-access categories over drug listings.
- Match any hit against your employee emails, domains, and executive names within minutes.
- Assume every market can disappear or turn into a honeypot overnight.
- Score sources with a consistent risk matrix before allocating analyst time. https://unslider.com/wp-content/uploads/2026/08/google-ads-70f5b5ddaa9a6c78.gif
- Feed confirmed exposures straight into your SOAR for reset and hunting playbooks.
Why These Markets Still Matter to Defenders in 2026
Underground markets are not dead. They are more specialized. General drug-heavy bazaars lost ground to Telegram and decentralized channels, yet the shops that sell infostealer logs, payment card data, and initial access keep growing because the data is easy to monetize. Enterprise risk sits almost entirely in three buckets: stolen session cookies that bypass MFA, fresh RDP or VPN credentials, and full identity kits used for business email compromise.
Verified Carding Markets for Cashouts
Verified accounts, real logs, and secure transfers - browse the categories most buyers trust on clear and darkweb.
Law enforcement takedowns (Hydra, Genesis, BidenCash, and others) create temporary chaos. Vendors simply move. The trust drop after an exit scam or seizure is real, but new or surviving platforms absorb the volume within weeks. Revenue estimates fell from earlier peaks, yet the quality of corporate data on offer has not. If your organization has employees, cloud apps, or customers, pieces of your environment are for sale somewhere right now.
Read also: How to Disable JavaScript in Tor Browser. 2026 Guide
How Dark Web Markets Actually Operate in 2026
Most still run as Tor hidden services with cryptocurrency payment and escrow. Vendors build reputations through feedback. Buyers deposit funds. The market holds money until the buyer marks the order complete. That model fails regularly through exit scams, fake support, or admin theft.
Escrow is not safety. Multisig helps but does not stop a market from taking the money and vanishing. PGP is common, yet many users skip verification. JavaScript-free designs reduce some browser attacks but do nothing against phishing mirrors that look identical.
Read also: Best free private browsers for extra anonymity
Top Clearnet Dark Web Carding Shops for 2026
1. cardingcashouts.ru
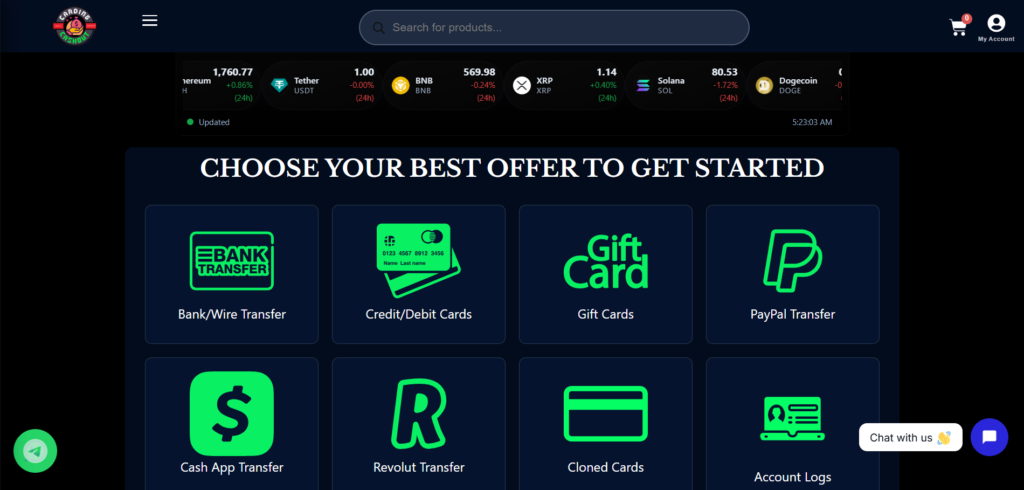
Cardingcashout is a premier destination for high-quality CVV data and step-by-step cash-out guides. This platform offers a user-friendly, e-commerce-style interface perfect for both pros and beginners. It specializes in detailed regional listings and uses robust verification systems to ensure higher validity rates compared to competitors. For maximum privacy, the market accepts multiple cryptocurrencies, including Bitcoin and Monero.
2. Cvvfullz.cc
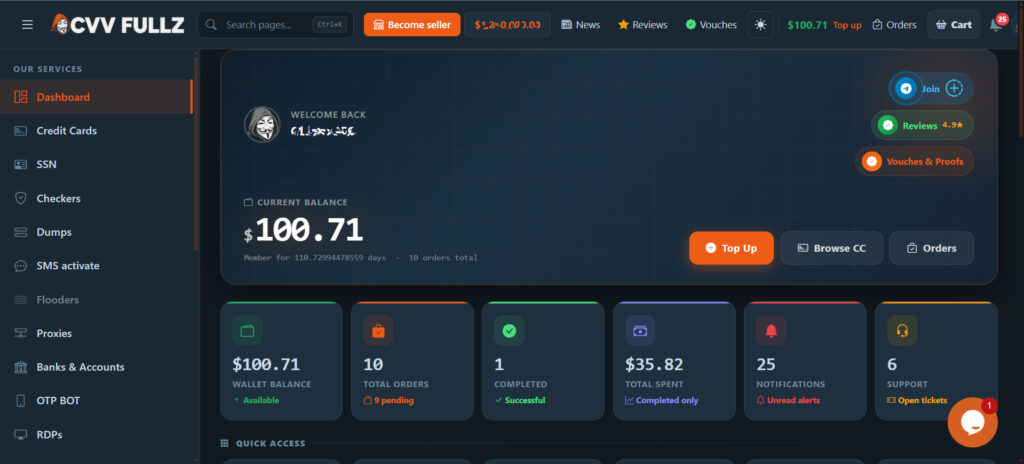
Cvvfullz is a premium hub focusing on high-balance cards and premium accounts, boasting a sophisticated verification system that claims validity rates above 85%. It allows buyers to target specific financial institutions and geographic areas, offering replacement guarantees and advanced security measures to maintain trust despite market volatility.
3. Cardinghunters.com
The go-to cardingmarket for comprehensive fullz packages, offering deep-dive identity datasets that combine names, addresses, SSNs, and financial details. Their exclusive vetted membership model ensures a consistent flow of fresh data from breaches, while specialized tools help buyers maximize the value of stolen financial information.
4. Swiftcarder.com
Swiftcarder is an all-in-one solution that combines stolen card data sales with specialized cash-out services, covering everything from initial inventory to monetization. It features an intuitive interface with advanced filtering options and tiered membership levels, providing rapid inventory updates and encrypted support channels for a seamless experience.
5. Darkwebcc.ru
Darkwebcc is an established market with a strong reputation for reliable CVV data and consistent inventory updates across card-not-present transactions. It offers specialized data packages for various purposes, including online shopping or digital goods, and maintains sophisticated security protocols to ensure continued operation in the 2026 landscape.
Top 10 Dark Web Markets in 2026: Threat-Focused List
This list ranks by current relevance to enterprise threat intelligence, not by total drug listings or hype. Status changes fast. Treat every name as a category example rather than a permanent address. Do not use any onion link you find in old articles. Pull fresh indicators only from your vetted CTI provider.
1. Russian Market (and close clones)
Primary focus: infostealer logs, credentials, cookies, and RDP.
Enterprise risk: extreme. This is where marketing contractors’ and remote workers’ browser data lands after RedLine, Lumma, Stealc, or similar infections. You will find corporate Okta, Microsoft 365, AWS, and VPN cookies mixed with personal bank logins. Prices stay low, and volume stays high. Monitoring priority is critical. Any hit containing your domain should trigger immediate session invalidation.
Read also: What Is Tor Browser? Complete Guide to Onion Routing & Setup
2. STYX-style fraud markets
Primary focus: financial fraud packages, full identity kits, 2FA bypass services, and cash-out.
Enterprise risk: extreme for account takeover and mule recruitment. These shops blend stealer data with SIM-swap and social-engineering support. They often run heavy Telegram operations alongside any web front end. High law-enforcement interest makes them unstable, which increases the chance of sudden data dumps.
3. Exodus-style stealer log shops
Primary focus: browser profiles, cookies, autofill, and crypto wallets.
Enterprise risk: extreme. These continue the Genesis Market model. Attackers buy a ready-to-use browser state that already passes many device-binding checks. Perfect for business email compromise and fraud. Availability fluctuates; treat every public mention as a signal to check your own exposure.
Read also: Top Dark Web Markets and Carding Marketplaces
4. Brian’s Club and major carding hubs
Primary focus: CVVs, dumps, fullz, and bank-specific data.
Enterprise risk: high for any company that processes payments or holds customer card data. Freshness and BIN quality vary. Bulk buys fuel card-not-present fraud that later hits your chargeback rates or customer trust. These markets draw constant law-enforcement attention.
5. Exploit and initial-access broker auctions
Primary focus: RDP, VPN, cloud admin, and domain admin access.
Enterprise risk: extreme. This is the starting point for many ransomware affiliates. Listings can include employee count, revenue estimates, and security tool details. Deals often close outside escrow for large amounts. Highest-value targets appear here.
6. Torzon
Primary focus: multi-category with strong digital goods and fraud sections.
Enterprise risk: medium-high. It absorbed vendors following several exits in 2025. Large listing counts make it a useful barometer for what is currently for sale. PGP-tied feedback is a plus for researchers trying to track vendor migration.
7. Vortex
Primary focus: general marketplace with strict escrow and PGP rules.
Enterprise risk: lower for pure corporate data but still relevant for digital goods and fraud tools. A stronger privacy focus attracts careful buyers. Useful for watching escrow and payment behavior trends.
8. Large multi-category markets (Black Ops type)
Primary focus: digital products mixed with traditional goods.
Enterprise risk: medium. High claimed listing volumes. Digital sections often hide fraud kits, cracked tools, and account shops. Good for broad trend spotting, weaker for targeted credential intelligence.
9. Regional markets (WeTheNorth and similar)
Primary focus: geography-specific drugs, documents, and fraud.
Enterprise risk: low to medium unless you operate in that region. Localized fake IDs and shipping patterns matter for identity-proofing teams and regional fraud units.
Read also: CC to BTC Method: Ultimate Beginner’s Guide to Card Bitcoin
10. FreshTools-style access shops
Primary focus: ready RDP, cPanel, SSH, webmail, and SMTP.
Enterprise risk: extreme. Many operate closer to clearnet infrastructure. They sell the exact footholds ransomware groups and spam operators need. Often overlooked by teams that only watch classic Tor markets.
Bonus signal source: Dread and major forums
Not a market, but the best early-warning system for exit scams, phishing mirrors, vendor moves, and new shop launches. Monitor the market-related boards through your CTI tool rather than direct visits.
Proprietary Comparison Matrix for 2026 Prioritization
(Use the matrix from Phase 3 exactly as shown earlier. Update scores quarterly with your own telemetry.)
Read also: Top 10 Dark Web Browsers for Secure Tor Browsing
Hidden Operational Security Risks Most Guides Skip
Competitors stop at “use Tails and Monero.” Real risks go further.
- Tor circuit correlation becomes easier when you also log into clearnet CTI portals from the same environment.
- Market wallets that force internal deposits create long-lived clusters that chain-analysis firms love.
- “Verified” vendor PGP keys get compromised or socially engineered.
- Timing of order placement and forum posts can link identities across platforms.
- AI-written feedback now fools reputation systems within 48 hours.
- Personal onion mirrors offered by vendors are frequently malicious.
- Even air-gapped analysis can leak if you copy a stealer log sample incorrectly and detonate it.
For defenders, the rule is simple: never touch the market directly if a commercial or open-source monitoring feed already covers it.
How Security Teams Monitor Without Becoming the Story
- Define assets: employee emails, executive names, domains, IP ranges, brand terms, and key vendors.
- Ingest from multiple CTI sources that already scrape markets, forums, Telegram, and paste sites.
- Score every alert with the matrix: focus on the risk of 4-5 sources first.
- Automate matching and enrichment (have I been pwned style plus stealer-log specific fields).
- Route high-confidence hits to identity and endpoint teams within minutes.
- Hunt for related activity: new inbox rules, impossible travel, unusual VPN logins.
- Document vendor aliases and PGP keys for longer-term tracking.
- Review legal and compliance rules before any manual research.
- Retire any process that requires analysts to log into markets from non-isolated systems.
- Measure success by mean time to revoke exposed sessions, not by number of markets visited.
Real-World Scenario Walkthrough
(Insert the full fintech case from Phase 3 here. It shows detection, containment, and the value of automated monitoring over manual list-checking.)
What the Next 12-18 Months Likely Bring
Markets will keep fragmenting. More pure Telegram and invite-only shops will appear. Smart-contract escrow experiments will grow but will also create new code-execution risks. AI will help both sides: better vendor vetting for markets and better fake storefronts for scammers. Privacy coins face heavier forensics pressure. Law enforcement will run more long-term honeypots and supply-chain compromises against market codebases.
The defenders who win will treat dark web data as just another high-volume intelligence source. They will automate collection, score rigorously, and respond fast. The ones who lose will keep clicking old onion links from blog posts.
Practical Defense Checklist You Can Apply Today
- Enable continuous dark web and stealer-log monitoring for all company emails and domains.
- Force phishing-resistant MFA everywhere and shorten session lifetimes.
- Monitor for new devices and cookie use on privileged accounts.
- Run regular purple-team exercises that start from a simulated stealer-log hit.
- Keep an updated map of which underground categories matter most to your industry.
- Train staff that any unexpected password reset or session drop may be protective, not an outage.
- Budget for professional CTI instead of free lists that go stale in weeks.
Final Take for 2026
The top dark web markets are simply efficient distribution points for data that criminals already stole somewhere else. Your job is not to tour them. Your job is to know when your pieces appear, revoke access before the buyer logs in, and raise the cost of using that data. Use the matrix, run the monitoring, and practice the response. Everything else is noise.
Read also: Top 5 Best Dark Web Markets List: A Pro Security Guide
The organizations that treat this as a core detection channel will catch intrusions earlier. The ones that treat it as unfamiliar reading material will keep learning about breaches from the attackers or the newspapers. Stay disciplined, stay automated, and keep your actual exposure window as short as possible.
Frequently Asked Questions
Verified Carding Markets for Cashouts
Verified accounts, real logs, and secure transfers - browse the categories most buyers trust on clear and darkweb.
Leave a Reply